September 2026 CVE Landscape

October 13, 2026
5 min read
719 views

In September 2026, Insikt Group® identified 94 high-impact vulnerabilities to prioritize for remediation, 59 of which had a Very Critical Recorded Future Risk Score. This represents a 29% increase from last month. 43 of these vulnerabilities were surfaced through the US Cybersecurity and Infrastructure Security Agency (CISA)’s Known Exploited Vulnerabilities (KEV) catalog, 37 were reported in open sources and validated by Insikt Group, and 14 were exclusively surfaced through honeypot data.

The 94 vulnerabilities identified affected products from 58 vendors, with Linux and Microsoft together accounting for approximately 13% of the vulnerabilities. The remaining exposures spanned network edge and security management appliances; operating systems (OS) and mobile devices; collaboration, content management, and enterprise platforms; artificial intelligence (AI), developer, and automation tools; and operational technology and industrial systems.

September reporting also highlighted zero-day exploitation of CVE-2026-88771 and CVE-2026-88772 (NetScaler), as well as renewed exploitation of CVE-2026-35273 (PeopleSoft) against unpatched systems.

Quick reference: September 2026 vulnerability table

All 80 vulnerabilities below were actively exploited or operationally weaponized in September 2026. This table does not include the 14 CVEs that were exclusively surfaced through honeypot data, which are available to Recorded Future Intelligence Platform customers via the CVE Monthly report. The table below also provides examples of public PoCs identified by Insikt Group. These PoCs were not tested for accuracy or efficacy. Vulnerability management teams should exercise caution and verify the validity of PoCs before testing.

#
Vulnerability
Risk
Score
Vendor/Product
KEV
RCE
PoC
1
CVE-2019-0708
99
Microsoft Remote Desktop Services
✓
2
CVE-2021-38003
99
Google Chrome
✓
3
CVE-2021-44228
99
Apache Log4j2
✓
4
CVE-2022-0847
99
Linux kernel
5
CVE-2022-22965
99
Spring Framework
✓
6
CVE-2025-25249
99
Fortinet FortiOS and FortiSwitchManager
✓
✓
7
CVE-2025-39682
99
Linux kernel (Siemens SIMATIC CN 4100)
✓
8
CVE-2025-39964
99
Linux kernel (Siemens SIPLUS S7-1500 CPU 1518-4 PN/DP MFP)
✓
9
CVE-2026-19490
99
Citrix NetScaler ADC and Gateway
✓
10
CVE-2026-20079
99
Cisco Secure FMC and SCC Firewall Management
✓
✓
11
CVE-2026-39987
99
Marimo
✓
12
CVE-2026-42016
99
JFrog Artifactory
✓
13
CVE-2026-42018
99
JFrog Artifactory
✓
14
CVE-2026-48710
99
Starlette and affected Red Hat products
✓
15
CVE-2026-49869
99
Kestra OSS
✓
✓
16
CVE-2026-53266
99
Linux kernel
✓
17
CVE-2026-5430
99
WSO2 Universal Gateway, Traffic Manager, and API Control Plane
✓
18
CVE-2026-58704
99
Google Pixel (modem)
✓
19
CVE-2026-60137
99
WordPress Core
20
CVE-2026-63030
99
WordPress Core
✓
21
CVE-2026-65660
99
Microsoft SharePoint Server
✓
✓
22
CVE-2026-67277
99
MikroTik RouterOS
✓
23
CVE-2026-67279
99
MikroTik RouterOS
✓
24
CVE-2026-71362
99
Adobe Commerce and Magento Open Source
✓
25
CVE-2026-7273
99
Zyxel GS1900 series switches
✓
✓
26
CVE-2026-75650
99
Adobe Commerce and Magento Open Source
✓
✓
27
CVE-2026-76460
99
Cisco ISE and ISE-PIC
✓
28
CVE-2026-76461
99
Cisco Secure Email Gateway
✓
✓
29
CVE-2026-76504
99
Cisco Catalyst SD-WAN Manager
✓
30
CVE-2026-81963
99
Microsoft Windows Update Stack
✓
31
CVE-2026-83548
99
SonicWall SMA1000
✓
32
CVE-2026-84869
99
ConnectWise ScreenConnect
✓
✓
33
CVE-2026-85102
99
Check Point Security Gateway and Spark Firewall
✓
✓
34
CVE-2026-85706
99
GitLab CE/EE
✓
35
CVE-2026-85880
99
Microsoft Windows ALPC
✓
36
CVE-2026-86060
99
MikroTik RouterOS
✓
37
CVE-2026-86218
99
N-able N-central
✓
✓
38
CVE-2026-86950
99
Apple iOS, iPadOS, and macOS
✓
✓
39
CVE-2026-87491
99
Google Chrome (V8)
✓
✓
40
CVE-2026-87886
99
Acronis Backup integrations for cPanel & WHM, Plesk, and DirectAdmin
✓
41
CVE-2026-87902
99
WordPress Core
✓
✓
42
CVE-2026-88771
99
Citrix NetScaler ADC and Gateway
✓
✓
43
CVE-2026-88772
99
Citrix NetScaler ADC and Gateway
✓
✓
44
CVE-2026-93616
99
Check Point Management Server
✓
✓
45
CVE-2026-93952
99
Arista VeloCloud Orchestrator
✓
46
CVE-2026-94127
99
F5 BIG-IP APM
✓
✓
47
CVE-2014-6271
89
GNU Bash
✓
48
CVE-2020-1938
89
Apache Tomcat
✓
49
CVE-2021-43798
89
Grafana
50
CVE-2024-21762
89
Fortinet FortiProxy and FortiOS
✓
51
CVE-2026-20316
89
Cisco Secure Firewall Management Center (FMC)
52
CVE-2026-34908
89
Ubiquiti UniFi OS
53
CVE-2026-34909
89
Ubiquiti UniFi OS
54
CVE-2026-34910
89
Ubiquiti UniFi OS
✓
55
CVE-2026-35273
89
Oracle PeopleSoft Enterprise PeopleTools
✓
56
CVE-2026-59822
89
LiteLLM
✓
57
CVE-2026-60004
89
Gitea
✓
58
CVE-2026-81578
89
PaperCut NG/MF
59
CVE-2026-82078
89
PaperCut NG/MF
60
CVE-2026-82329
89
JFrog Artifactory
✓
61
CVE-2026-83549
89
SonicWall SMA1000
✓
✓
62
CVE-2026-85046
89
Google Chromium V8 and Chrome
✓
✓
63
CVE-2026-89026
89
Issabel Framework
✓
64
CVE-2026-9586
89
Sangoma Switchvox SMB Edition
✓
✓
65
CVE-2023-54391
87
Proxmox Virtual Environment (VE)
66
CVE-2026-56271
84
Flowise
67
CVE-2026-86124
83
HKUDS AutoAgent
✓
68
CVE-2026-67394
82
WebPros Plesk
✓
69
CVE-2016-4437
79
Apache Shiro
✓
70
CVE-2021-29441
79
Alibaba Nacos
71
CVE-2024-4956
79
Sonatype Nexus Repository
72
CVE-2026-14894
79
Super Forms for WordPress
✓
73
CVE-2026-27540
79
WooCommerce Wholesale Lead Capture for WordPress
✓
74
CVE-2026-32475
79
Elementor Pro for WordPress
✓
75
CVE-2026-51990
79
Sogou Input Method
✓
76
CVE-2026-67276
79
MikroTik RouterOS
77
CVE-2026-54569
73
Senaite
✓
78
CVE-2026-58046
71
WebPros Plesk
79
CVE-2026-64637
71
WebPros Plesk
80
CVE-2026-79756
71
Nuclio
✓

Table 1: List of vulnerabilities that were actively exploited in September 2026 based on Recorded Future data (excluding honeypot-sourced CVEs).

Key trends: September 2026

  • September reporting linked NightEagle and UNC3569 to GhostContainer and GRAYRABBIT deployments, while Cisco FMC exploitation by three threat clusters led to credential theft, Cyclops Blink deployment, and Qilin ransomware.
  • A suspected Chinese-speaking actor used a SecFlow-based environment with Claude-, Qwen-, and DeepSeek-backed workers, and a suspected Russian-speaking actor used hundreds of AI agents to compromise at least 440 PaperCut NG/MF instances associated with 395 organizations.
  • 47 of the 94 vulnerabilities enabled remote code execution (RCE). Network-edge and security-management products were the most affected product type. Apache and Google represented the largest share of vendors, with three RCE vulnerabilities each.
  • Insikt Group identified public proof-of-concept (PoC) exploits or scanners for 75 of the 94 vulnerabilities identified in September.
  • The most common weakness class was CWE-306 (Missing Authentication for Critical Function), with seven vulnerabilities, followed by CWE-22 (Path Traversal), with six. CWE-78 (OS Command Injection), CWE-89 (SQL Injection), and CWE-94 (Code Injection) each affected five vulnerabilities.
  • Eight of the 94 vulnerabilities were at least five years old, and the oldest was approximately 12 years old.

Trend analysis

AI-assisted campaigns combine older flaws with post-compromise tooling

Insikt Group detailed a suspected Chinese-speaking actor using a SecFlow-based operations environment with Claude-, Qwen-, and DeepSeek-backed workers to support reconnaissance, exploitation, post-exploitation, and collection across Asian targets. The threat actor tested or staged workflows for CVE-2014-6271, CVE-2020-1938, CVE-2022-22965, CVE-2016-4437, CVE-2021-43798, CVE-2024-4956, CVE-2021-29441, and CVE-2021-44228. The workflow routed candidate findings to vulnerability-specific playbooks, but not every attempt produced confirmed access.

A separate September report described a suspected Russian-speaking threat actor using hundreds of AI agents in a campaign targeting PaperCut NG/MF. The campaign exploited CVE-2026-81578 and CVE-2026-82078, compromising at least 440 instances associated with 395 organizations.
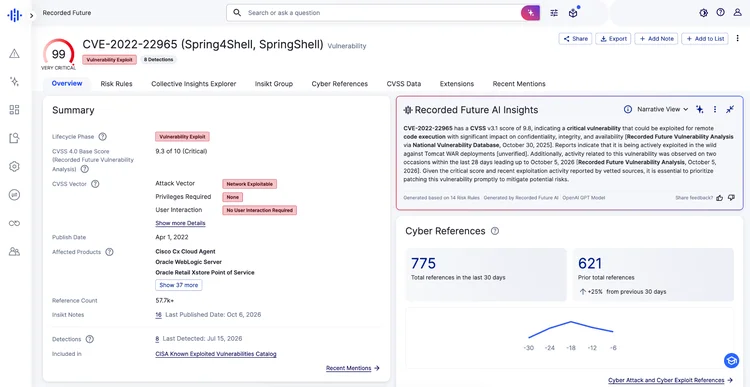
Risk Rules history on the Vulnerability Intelligence Card® for CVE-2022-22965 in Recorded Future
Figure 1: Risk Rules history on the Vulnerability Intelligence Card® for CVE-2022-22965 in Recorded Future (Source: Recorded Future)
Source: James Rodriguez · www.recordedfuture.com

Comments

Sign in to comment.
No comments yet. Be the first to comment.